
Kaspersky has released a report about a phishing campaign where attackers abuse Microsoft’s authentication mechanism. The campaign spanned from early April to mid-May 2026 and was styled as a notice from a law firm. The goal was to steal victims’ credentials and access their data. Previously Kaspersky warned about phishing exploiting Google Tasks, Google Forms, Bubble and Amazon Simple Email Service.
Microsoft’s authentication mechanism – the OAuth 2.0 Device Authorisation Grant – allows users to log into their Microsoft accounts on devices with limited input capabilities, such as smart TVs, by pasting a code or scanning a QR code on another device, like a smartphone or a PC. This convenience also creates an opportunity for attackers to abuse the flow, potentially hijacking accounts and maintaining control through stolen refresh tokens.
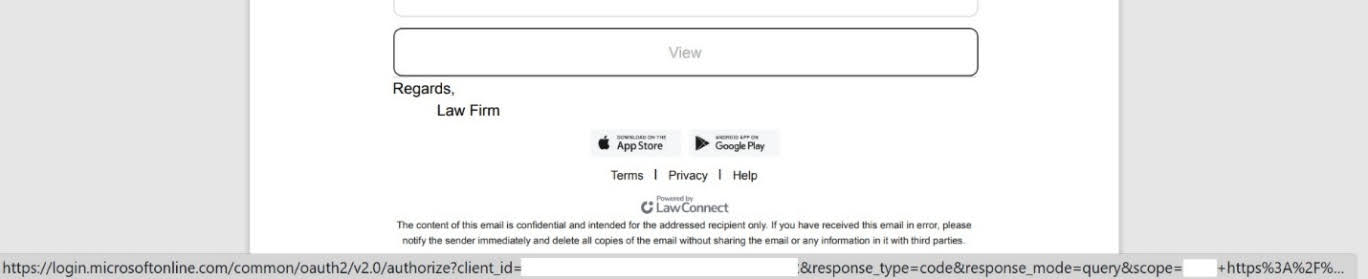
Attackers sent victims emails disguised as communication from a law firm, with a password-protected PDF file attached. After opening the PDF and entering the password, they were presented with a webpage that listed several documents. Viewing these documents required clicking a provided link, which led to a legitimate Microsoft address. However, the URL parameters were configured to redirect the user to a phishing resource after they opened the Microsoft page.
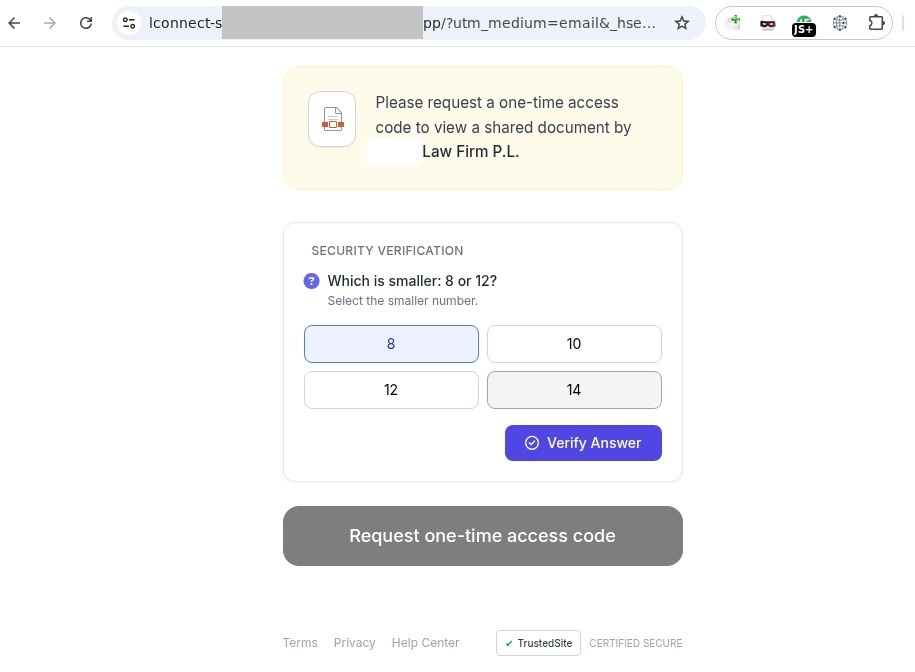
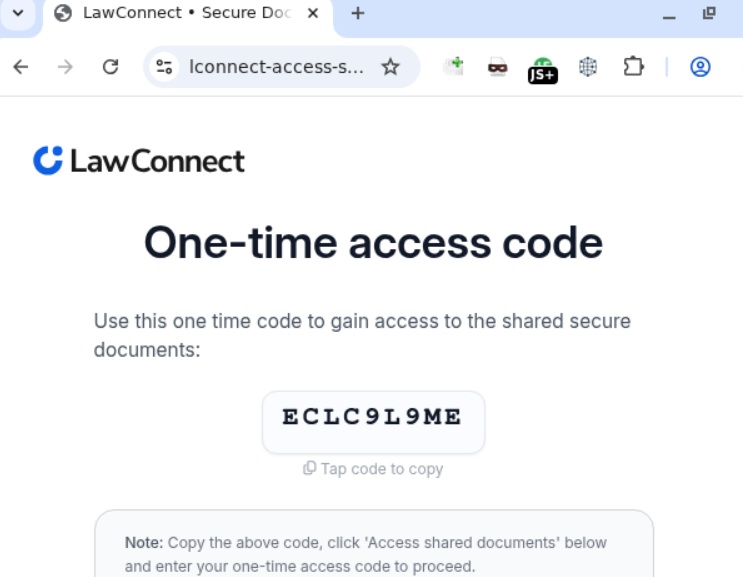
The phishing page featured multiple CAPTCHAs, presumably deployed to filter out security bots which are used to check websites for threats. Once past the CAPTCHAs, the user was routed to a final page that instructed them to copy a one-time code. This code was the one that the attackers had already fetched by starting the login process on their side.
Clicking the displayed one-time code automatically copied it to the clipboard while simultaneously redirecting the user to Microsoft’s actual, legitimate authentication page where they were prompted to paste and enter the code.
After the user entered the code, the multifactor authentication process completed and the attackers got hold of the session’s tokens. This enabled them to read and send emails from the victim’s mailbox, exfiltrate files from OneDrive and access Teams conversations.
“Threat actors don’t always rely on harvesting credentials or deploying malware to access sensitive data – they can weaponise legitimate tools. Therefore, users must exercise vigilance not only when visiting suspicious sites, but also when navigating official platforms. We advise enterprise teams to evaluate the business necessity of the Device Code Flow within their corporate infrastructure. If this authentication mechanism is not required for daily operations, it should be disabled,” commented Roman Dedenok, Anti-Spam Expert at Kaspersky.
To establish a comprehensive defence against Device Code Phishing attacks, organisations should deploy robust email security solutions. For corporate users, Kaspersky Security for Mail Server with its multi-layered defence mechanisms powered by machine learning algorithms provides robust protection against a wide range of evolving threats and offers peace of mind to businesses in the face of evolving cyber risks. For individual users, Kaspersky Premium offers AI-powered anti-phishing features designed to help avoid phishing attacks and improve overall cybersecurity.