
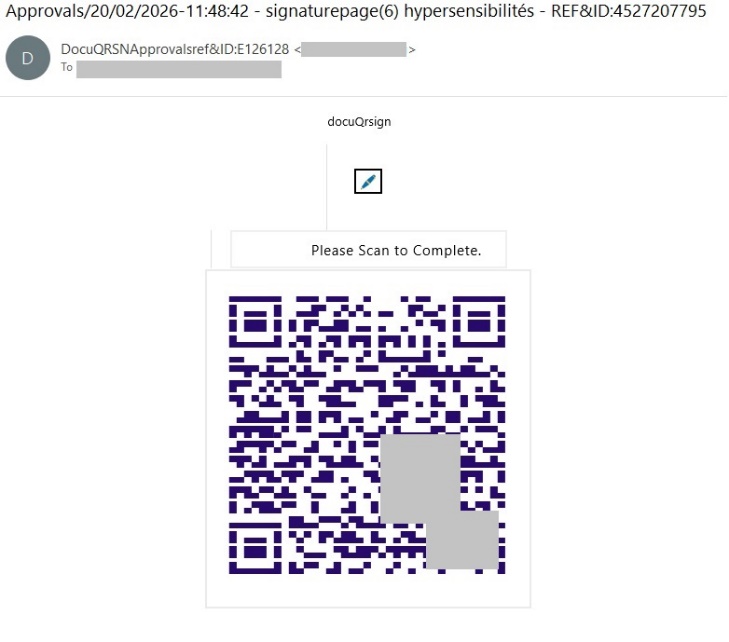
QR codes embedded in emails have long been a tool for phishing and scams, and back in the second half of 2025 there was a fivefold surge in QR phishing attacks detected by Kaspersky. Now Kaspersky researchers have identified a new phishing tactic in which attackers construct QR codes using text characters rather than traditional images. This method allows such malicious QR codes to bypass many email security solutions that rely on image scanning or link detection.
Early computers were incapable of rendering true graphics, and images on them were composed entirely of text characters. Historically this was done with symbols from the ASCII (American Standard Code for Information Interchange) character set, introduced in 1963. Images created using this technique were called ASCII graphics. Later other character sets (like Unicode) were also utilised to create images, but the term ASCII graphics remained.
In the 2000s, spam senders already used images built from text symbols. By using text-based graphics instead of embedded images, attackers tried to avoid detection mechanisms that analyse pictures for hidden URLs.
With ASCII graphics used to create QR codes, the phishing scheme follows a familiar pattern as with QR codes in images which Kaspersky described earlier. Victims receive an email allegedly coming from a business partner, claiming to include a confidential document for signature via DocuSign. The message instructs the recipient to scan a QR code to access the document, leading to a fake website where corporate credentials are requested. With the QR code laid out in text characters, many protective solutions would fail to identify any suspicious links.

“We have previously seen phishers try to avoid link scanning by hiding URLs in images. Now they are attempting to evade image-based scanning by returning to text – this time to render a QR code. Any instance where a QR code prompts someone to enter corporate credentials on a mobile device should raise immediate suspicion. When the QR code is formed using textual ASCII art, it is almost certainly a phishing attempt or a lure to a malicious URL. This trick has only one purpose: bypassing security technologies,” comments Roman Dedenok, Anti-Spam Expert at Kaspersky.
To defend against this threat, Kaspersky recommends deploying a proven mail server security solution such as Kaspersky Security for Mail Server that provides secure corporate email exchange, countering spam, email-borne infections, all forms of phishing, business email compromise (BEC), QR code attacks, and other threats.