
Cloud technology has fundamentally changed how organisations operate, delivering unprecedented flexibility, scalability, and speed. Yet despite years of cloud adoption and growing familiarity with cloud environments, security remains one of the most significant concerns for businesses moving their operations and data online.
The reason is surprisingly simple: while the technology has changed, the fundamentals of security have not.
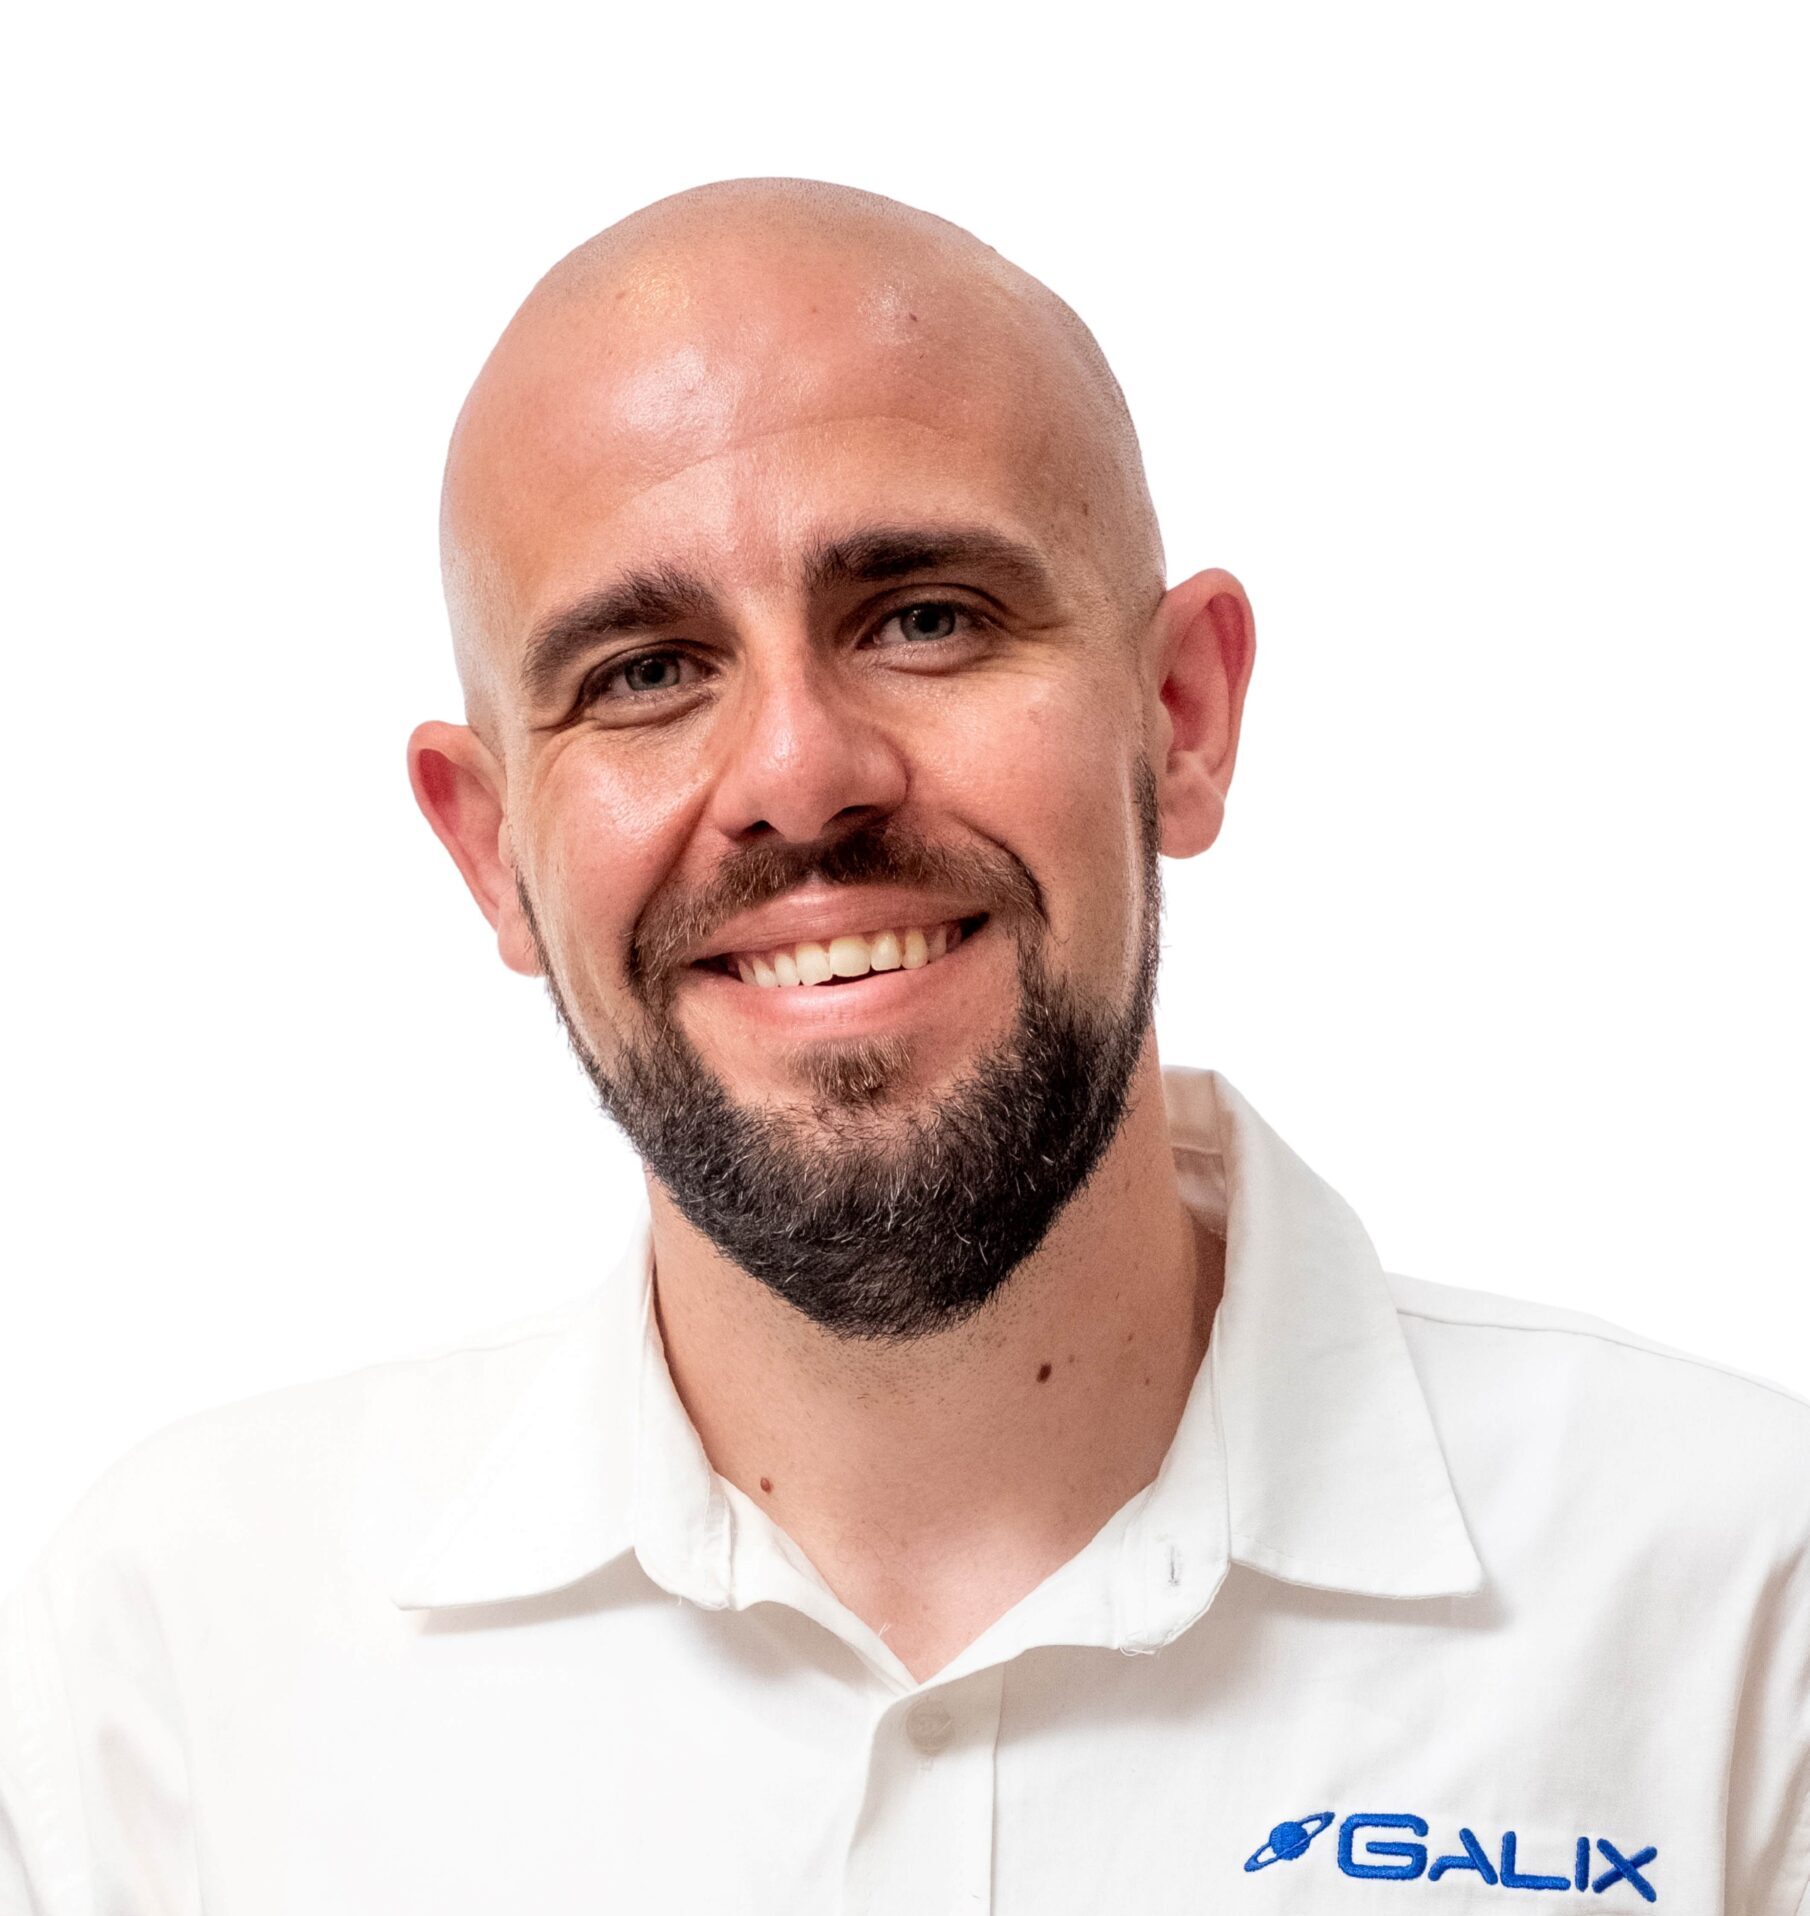
“The cloud is really just a newfangled word for something that’s always existed,” says Ryan Boyes, Senior Security Administrator at Galix. “Your data is still sitting on a hard drive somewhere, and that means it’s still potentially accessible to people who shouldn’t have it.”
This misconception lies at the heart of many cloud security challenges. Organisations often assume that migrating to a major cloud provider automatically transfers responsibility for security to that provider. In reality, cloud adoption changes how security is managed rather than eliminating the need for it.
One of the most common pitfalls is the failure to properly assess and manage risk before implementation. Businesses are frequently drawn to the speed and convenience of cloud services but overlook the governance, compliance, and security processes required to support them.
Boyes compares it to workplace safety. “If you’re equipping a miner, have you given them the right training and gear? You can’t guarantee they’ll never get injured, just like you can’t guarantee a system won’t be breached. But as an organisation, you have a responsibility to show you did everything reasonably possible beforehand.”
When strategy struggles to keep pace
The consequences of poor planning often surface through misconfigurations, shadow IT, and inadequate oversight. Shadow IT, where employees deploy unauthorised applications or services outside official company controls, can create significant blind spots for security teams. Misconfigured cloud environments can expose sensitive information to unintended audiences, while weak governance structures make it difficult to identify and address risks before they become incidents.
According to Boyes, these issues rarely stem from technology itself. “We see this in audits constantly. A company passes their first year, then fails the second because their documentation says they run monthly scans, but they can’t produce twelve months of records. The document describes what they should do; they’re just not doing it.”
This highlights a broader challenge facing many organisations: security strategies are not evolving at the same pace as cloud adoption.
Businesses continue to embrace cloud services to gain competitive advantages through greater agility and faster deployment. However, the security maturity required to support that growth often lags behind. Rather than proactively identifying risks, many organisations find themselves responding to problems after they occur.
“A genuinely proactive strategy starts with a risk assessment before anything gets implemented,” says Boyes. “You don’t want to build on a weak foundation, because once it’s built, that’s what everything else rests on.”
The challenge is compounded by an ongoing cybersecurity skills shortage. Building an effective cloud security strategy requires experienced professionals who understand both the technology and the evolving threat landscape.
The hidden risks of public cloud environments
The growing reliance on public cloud services introduces additional considerations. While public cloud platforms offer significant cost advantages, they also create new risk exposures that organisations must understand and address.
Data exposure remains one of the most obvious concerns. Public-facing environments naturally present opportunities for unauthorised access if controls are not properly configured and monitored. Vendor lock-in can also become problematic, leaving businesses dependent on providers that may no longer align with their requirements but are too costly or complex to replace.
Adding to this is the sheer size of the attack surface. Modern cloud environments typically consist of multiple APIs, endpoints, integrations, and interconnected services, each representing a potential entry point for attackers.
“The public cloud option may be more affordable, but what level of security are you giving up?” Boyes asks. “What risks are you introducing, and how are you going to close those gaps?”
The answer is not necessarily to avoid public cloud altogether. Rather, organisations need to fully understand the trade-offs involved and develop plans to mitigate the risks associated with their chosen platforms.
Complexity grows as cloud services evolve
The complexity increases further when organisations adopt Infrastructure-as-a-Service (IaaS) and Platform-as-a-Service (PaaS) environments. While both offer significant benefits, they also create shared responsibilities that can be difficult to manage if roles and boundaries are not clearly defined.
IaaS provides extensive flexibility, allowing organisations to configure infrastructure according to their needs. However, greater flexibility also means more opportunities for misconfiguration. PaaS simplifies certain operational tasks by managing operating systems, runtimes, and scalability, but introduces additional layers of interaction and dependency.
“The more configurable something is, the greater the chance of misconfiguration if it hasn’t been properly assessed,” says Boyes.
One of the biggest misconceptions surrounding these services is the belief that managed automatically means secure. “There’s a dangerous assumption that ‘managed’ means ‘secure’. It doesn’t,” he explains. “You don’t eliminate responsibility by outsourcing, you just change how it’s managed.”
This is where governance, risk, and compliance become just as important as technical expertise. Technical teams may focus on implementation and functionality, but organisations must also understand the legal, regulatory, and operational implications of the technologies they deploy.
For example, the growing integration of artificial intelligence capabilities into cloud platforms introduces new compliance considerations that many organisations are only beginning to explore. Questions around data usage, privacy, governance, and accountability require input from multiple stakeholders, not just technical teams.
Why expert guidance has become essential
Ultimately, successful cloud security requires organisations to bring technical and governance expertise together from the outset. Technology decisions cannot be made in isolation from risk management considerations.
“The most effective approach brings both skillsets into the room together,” concludes Boyes. “Technical expertise tells you what’s possible and how to implement it. Governance and risk expertise tells you what the implications are and whether you’re doing it responsibly.”
For many organisations, however, building and maintaining that breadth of expertise internally is becoming increasingly difficult. The pace of cloud innovation, evolving compliance requirements, growing cyber threats, and ongoing skills shortages mean that businesses often lack the resources needed to effectively manage every aspect of cloud security on their own.
As a result, partnering with experienced cybersecurity and governance specialists is becoming a strategic necessity rather than a luxury. Expert guidance helps organisations identify risks early, implement appropriate controls, maintain compliance, and establish the governance frameworks needed to support long-term cloud success.
Cloud technology can deliver significant business value, but only when it is supported by the right security foundations. By combining robust planning, continuous oversight, and specialist expertise, organisations can confidently embrace the benefits of the cloud while ensuring their data, systems, and operations remain secure.